Tag: dependency security

Security Teams Are Fixing Vulnerabilities Faster Than Ever. So Why Is Software Getting Riskier?
 Mitchell Johnson | | AI coding agents, AI Development, application security, automated remediation, CI/CD, dependency security, dependency selection, developer experience, devsecops, open source security, secure coding, secure software development, security policy, shift left security, software composition analysis, software risk, Software Supply Chain, technical debt, vulnerability backlog, vulnerability management
AI is speeding up dependency decisions, making point-of-selection security essential for reducing vulnerable components, downstream tickets and avoidable rework ...

DevSecOps Teams as Partners in Secure Software Delivery
 Manish Shetty | | application security, CI/CD, CI/CD security, dependency security, devops security, devsecops, risk management, secure software development, security automation, Security Guardrails, shift left security, software security, Software Supply Chain, vulnerability management
DevSecOps teams can reduce last-minute release delays by shifting security decisions earlier, improving guardrails, clarifying ownership and making findings actionable ...
Cycode Extends DevSecOps Reach to Software Packages Developers Download
 Mike Vizard | | ADLC, agentic development lifecycle, AI coding agents, cool down period, Cycode, dependency security, Developer Security, devsecops, malicious packages, package security, software repositories, Software Supply Chain Security, supply chain attacks, threat intelligence, workstation protection
Cycode is adding workstation-level protection to stop developers and AI coding agents from downloading malicious or insufficiently vetted software packages ...

Why Your CI/CD Pipeline Is Your Most Unprotected Attack Surface
 Muhammad Yawar Malik | | application security, build agents, build pipelines, CI/CD security, Cloud Security, credential security, dependency security, deployment security, devops security, devsecops, ephemeral runners, GitHub Actions, infrastructure security, Jenkins security, least-privilege, pipeline security, provenance attestation, secrets management, secure pipelines, secure software development, software provenance, Software Supply Chain, supply chain attacks, third-party actions, XZ Utils
CI/CD pipelines often hold privileged credentials, execute third-party code and connect directly to production, making pipeline security one of the most overlooked risks in modern DevOps ...
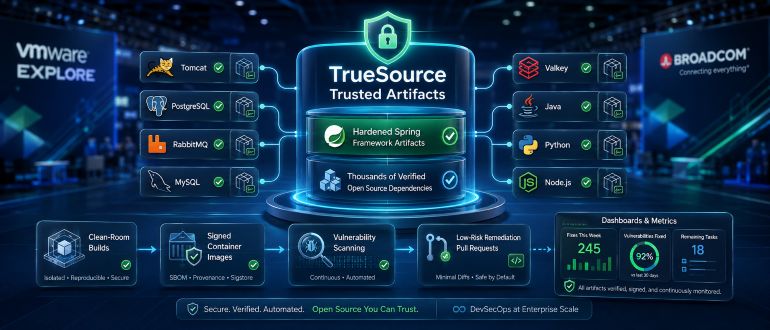
Broadcom Launches TrueSource Service to Secure Spring Framework
Mike Vizard | | AI coding, Apache Tomcat, application security, Bitnami Secure Images, Broadcom, container security, dependency security, devsecops, java, kubernetes, node.js, open source security, open source vulnerabilities, patch management, Python, SBoM, secure software development, software artifacts, Software Supply Chain Security, Spring framework, Spring Security, Tanzu, TrueSource Trusted Artifacts, VMware explore, vulnerability managementBroadcom launches TrueSource Trusted Artifacts to provide hardened Spring dependencies, secure open source packages and automated vulnerability remediation ...

Signed, Attested, and Malicious: The Software Supply Chain Has a Deepfake Problem
 Nigel Douglas | | AI coding agents, AntV packages, behavioural analysis, continuous scanning, dependency security, Developer Security, GitHub Actions compromise, malicious packages, Miasma worm, Mini Shai-Hulud, npm malware, OIDC tokens, open source security, package provenance, package quarantine, policy as code, Red Hat npm attack, registry scanning, Shai-Hulud worm, SLSA provenance, software attestation, Software Supply Chain Security, TanStack compromise, trusted pipeline attacks
A developer pulls a package from a reliable repo. It is signed, has provenance, and has been scanned. And then…it contains malware. That is no longer hypothetical. When the Miasma worm tore ...