Tag: least-privilege

Secrets Sprawl and Rotation: A Practical Vault Management Playbook
 Oreoluwa Omoike | | AI security, AI-assisted coding, API Key Security, AWS Secrets Manager, Azure Key Vault, CI/CD security, Cloud Security, credential exposure, Credential Rotation, Data Breaches, devsecops, Dynamic Secrets, GitGuardian, GitHub security, Google Secret Manager, hardcoded secrets, HashiCorp Vault, least-privilege, MCP Security, Model Context Protocol, non-human identities, secrets management, secrets sprawl, Security Boulevard, Terraform security
In 2025 alone, security firm GitGuardian detected 28.65 million new hardcoded secrets exposed in public GitHub commits — a 34% increase year over year and the largest single-year jump the company has ...
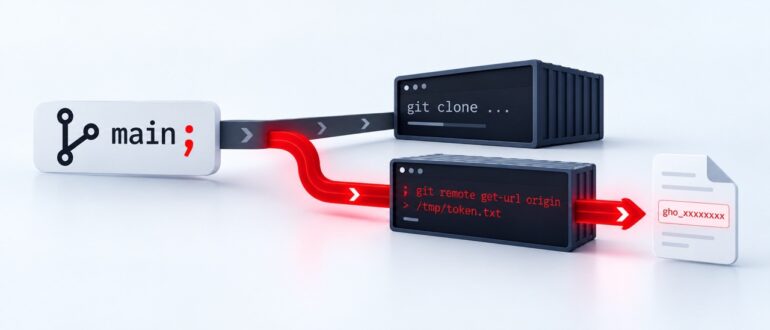
A Semicolon in a Branch Name Was All It Took to Steal an AI Agent’s GitHub Token
 Canio Campaniello | | AI agent security, command injection, credential security, GitHub security, least-privilege, OpenAI Codex
AI coding agents don't just suggest code anymore. Tools like OpenAI's Codex spin up a real container, clone a real repository, and authenticate with a real GitHub credential to get the job ...

GitHub Gives Enterprises a Full Count of Who Holds the Keys
 Tom Smith | | access management, agentic AI, AI coding agents, credential inventory, credential security, Developer Security, devsecops, github, GitHub Apps, GitHub Enterprise Cloud, identity security, least-privilege, OAuth tokens, PATs, Personal Access Tokens, secrets management, security operations, Software Supply Chain Security, SSH keys
GitHub Enterprise Cloud now lets organizations export a full inventory of credentials, helping security teams identify stale, overprivileged and forgotten access across users, apps and automation ...

Why Your CI/CD Pipeline Is Your Most Unprotected Attack Surface
 Muhammad Yawar Malik | | application security, build agents, build pipelines, CI/CD security, Cloud Security, credential security, dependency security, deployment security, devops security, devsecops, ephemeral runners, GitHub Actions, infrastructure security, Jenkins security, least-privilege, pipeline security, provenance attestation, secrets management, secure pipelines, secure software development, software provenance, Software Supply Chain, supply chain attacks, third-party actions, XZ Utils
CI/CD pipelines often hold privileged credentials, execute third-party code and connect directly to production, making pipeline security one of the most overlooked risks in modern DevOps ...

The Agent Proposes, the Pipeline Disposes: Controls for AI-Authored Change
 Veera Ravindra Divi | | agent permissions, agentic coding, AI change control, AI code review, AI coding agents, AI Governance, AI pull requests, AI software development, AI-authored code, AI-generated code security, autonomous coding agents, bounded-write agents, change-budget gates, CI/CD security, human-in-the-loop, in-toto, independent evals, least-privilege, policy as code, protected paths, provenance attestation, provenance verification, Secure DevOps, signed attestations, Sigstore, SLSA, Software Supply Chain Security, staged autonomy
When agents write code and open pull requests faster than humans can read them, ‘the diff looked fine’ stops being a control. The durable controls live outside the agent’s reasoning loop ...

15 DevSecOps Best Practices

DevOps is all about speed, agility and collaboration. But when it comes to security, DevOps teams often face unique challenges. From securing the application development process to protecting production environments, DevOps and ...

Infrastructure Access Management a Growing DevOps Priority
 Nathan Eddy | | agile infrastructure, Cybersecurity, devsecops, identity and access management, least-privilege
Organizations plan to address access management over the next 12 months, as the need to secure and streamline infrastructure-wide access controls serves as a prerequisite to other initiatives, like zero-trust. This was ...