Continuous Delivery

The DevOps Standard Gives Teams a Shared Model for Software Delivery
 Marc Hornbeek | | devops, DevOps Blueprint, devops institute, DevOps operating model, DevOps standard, nine pillars of devops
A release can pass every pipeline check and still leave an organization uncertain about whether to proceed. Security evidence may exist in another system, the recovery plan may be incomplete, and nobody ...

Talentica Software Unfurls Managed AI Service to Optimize Software Delivery

Talentica Software this week launched a managed software delivery service that leverages artificial intelligence (AI) to enable DevOps teams to deploy applications developed using AI coding tools at scale. Company CTO Manjusha ...

New npm Threat Bypasses Install Script Protections
A malicious npm package that has been downloaded millions of times comes with a new way of spreading the malware that makes it easier to bypass security protections, say researchers with security ...

Why Your CI/CD Pipeline Is Your Most Unprotected Attack Surface
 Muhammad Yawar Malik | | application security, build agents, build pipelines, CI/CD security, Cloud Security, credential security, dependency security, deployment security, devops security, devsecops, ephemeral runners, GitHub Actions, infrastructure security, Jenkins security, least-privilege, pipeline security, provenance attestation, secrets management, secure pipelines, secure software development, software provenance, Software Supply Chain, supply chain attacks, third-party actions, XZ Utils
CI/CD pipelines often hold privileged credentials, execute third-party code and connect directly to production, making pipeline security one of the most overlooked risks in modern DevOps ...
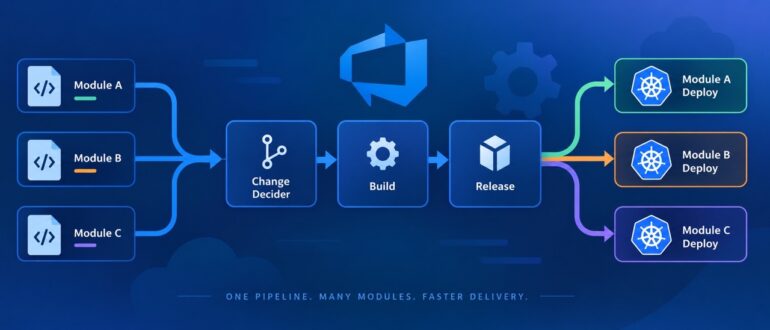
How I Consolidated Duplicate Delivery Pipelines With Parameters and Build Tags
 Ahmed Tariq | | Azure DevOps, build pipelines, CI/CD, deployment automation, devops, Release Pipelines
Two modules in a repository had near-identical Azure DevOps build and release definitions. A third would have required another pair. The delivery chain used five definitions: one change decider, two builds, and ...

Cloudsmith Extends Policies and Controls to Secure Application Binaries
Cloudsmith this week revealed it has expanded the policy management and continuous risk detection capabilities it makes available within its software artifact management platform to now include policy templates, cooldown policies, and ...

Fast-Moving Shai-Hulud Attack Infects npm Packages with 2 Billion Monthly Downloads
 Jeff Burt | | Aikido Security, AWS, credential theft, GitHub Actions, HashiCorp Terraform, npm malware, Shai-Hulud worm, supply chain attack
Researchers at Aikido Security and Endor Labs are tracking a fast-spreading supply-chain attack that is compromising a wide range of npm software packages that combined have more than 2 billion installs a ...

Building SOC 2 Compliant CI/CD Pipelines on AWS with GitHub Actions
 Artur Yolchyan | | Amazon ECR security, artifact traceability, AWS CI/CD pipeline, AWS compliance, AWS deployment pipeline, AWS multi-account architecture, CC6.1 access controls, CC7.1 vulnerability management, CC8.1 change management, container image promotion, cross-account ECR access, DevOps compliance, ECR lifecycle policies, ECR repository architecture, ECR scan on push, GitHub Actions OIDC, immutable artifacts, Secure software delivery, SOC 2 change management, SOC 2 CI/CD
How to design a secure, traceable AWS CI/CD pipeline using separate accounts, centralized ECR, OIDC and immutable image promotion for SOC 2 ...

FakeGit Targets AI Coding Agents with Malicious GitHub Repos
Jeff Burt | | AgentBaiting, AI coding agents, AI supply chain risk, Anthropic Claude Code, fake repositories, FakeGit, github, Google Gemini, Island, MCP Server, OpenAI ChatGPT, SmartLoader, StealCThreat actors continue to find new ways to incorporate AI into schemes aimed at luring developers into downloading malware from fake repositories. The latest example involves almost 7,600 malicious GitHub repositories that ...

GitHub API Abuse, ‘Ghost’ Accounts Part of Malicious Efforts to Map Organizations
Jeff Burt | | Cofense, Data Exfiltration, data mapping, data scraping, datadog, Fortran, GitHub API, GitHub ghost accounts, gitlab, GraphQL, personal tokens, REST APIsDatadog researchers uncover months-long overlapping campaigns to scrape data about companies and their developers ...
‘HalluSquatting’ Compromises AI Coding Agents to Install Malware, Create Botnets
Jeff Burt | | AI coding agents, AI hallucinations, AI security agents, Cursor, devops, GitHub Copilot, Google Gemini, HalluSquatting, indirect prompt injection, LLM, OpenClaw, promptwareHallucinations have been an ongoing problem since OpenAI first introduced its ChatGPT chatbot in November 2022, highlighting generative AI’s tendency to generate plausible but false or misleading information and its inability to ...

How to Build a DevSecOps CI/CD Pipeline on Azure With GitHub Actions
Fix security problems when they’re cheap to fix, which is before the code is deployed. A pipeline that enforces this automatically is what makes that principle real ...