Tag: vulnerability management

HackerOne Report Surfaces Massive Increase in Vulnerability Backlogs
 Mike Vizard | | AI security, AI vulnerability discovery, application security, appsec, bug bounty, cyber risk, Cybersecurity, devsecops, exploit development, exposure debt, HackerOne, output handling, prompt leakage, remediation backlog, security researchers, software security, vulnerability backlog, vulnerability management, vulnerability remediation, VulnOps
HackerOne research shows vulnerability remediation is getting faster, but AI-driven discovery is expanding exposure debt even more quickly, putting DevSecOps teams under growing pressure ...

Security Teams Are Fixing Vulnerabilities Faster Than Ever. So Why Is Software Getting Riskier?
 Mitchell Johnson | | AI coding agents, AI Development, application security, automated remediation, CI/CD, dependency security, dependency selection, developer experience, devsecops, open source security, secure coding, secure software development, security policy, shift left security, software composition analysis, software risk, Software Supply Chain, technical debt, vulnerability backlog, vulnerability management
AI is speeding up dependency decisions, making point-of-selection security essential for reducing vulnerable components, downstream tickets and avoidable rework ...
From Software Supply Chains to AI Vulnerabilities: Why Neither Solves Enterprise Linux Security
 Moshe Bar | | enterprise security, Linux security, patch management, runtime protection, runtime security, vulnerability management
For nearly a decade, cybersecurity has been dominated by one overarching concern: securing the software supply chain. Organizations invested heavily in Software Bills of Materials (SBOMs), artifact signing, provenance frameworks, reproducible builds, ...

DevSecOps Teams as Partners in Secure Software Delivery
 Manish Shetty | | application security, CI/CD, CI/CD security, dependency security, devops security, devsecops, risk management, secure software development, security automation, Security Guardrails, shift left security, software security, Software Supply Chain, vulnerability management
DevSecOps teams can reduce last-minute release delays by shifting security decisions earlier, improving guardrails, clarifying ownership and making findings actionable ...

More JFrog Artifactory Bugs Are Under Attack, and All Three Have Patches
 Tom Smith | | administrative tokens, artifact repositories, authentication bypass, build pipeline security, CI/CD security, CVE-2026-42016, CVE-2026-42018, CVE-2026-82329, Cybersecurity, devsecops, Groovy plugins, JFrog Artifactory, patch management, privilege escalation, Repository Security, Rust backdoors, Software Supply Chain, vulnerability management, web shells
Attackers are actively exploiting three JFrog Artifactory flaws, exposing how slow patching can turn artifact repositories into software supply chain attack paths ...
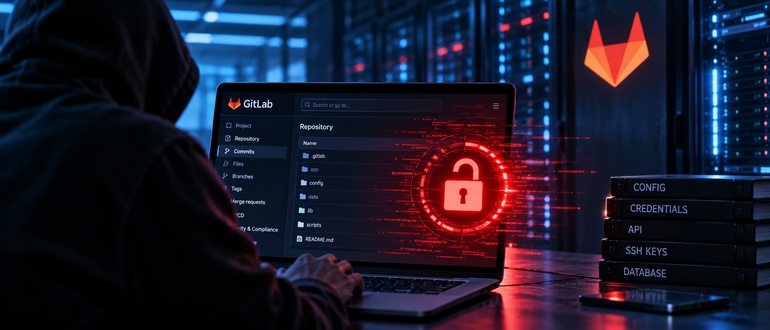
GitLab’s Critical Patch Closes a Path Traversal Flaw Attackers Are Already Probing
Tom Smith | | access control, API security, CI/CD security, credential theft, CVE-2026-85706, CVE-2026-87719, CVSS 10.0, Cybersecurity, devops security, devsecops, gitlab, GitLab Duo, GitLab security, GraphQL security, patch management, Repository Security, self-managed GitLab, Software Supply Chain, vulnerability managementGitLab patches two critical flaws, including a CVSS 10.0 unauthenticated file-read vulnerability, putting self-managed instances under urgent pressure to upgrade ...

Why AI Agents Shouldn’t Guess at Vulnerability Exploitability
 Harish Gaggar | | AI agents, application security, SBoM, Software Supply Chain, vulnerability management, vulnerability prioritization
Vulnerability prioritization is not a language problem. The safest agent architectures use models to interpret and explain, while deterministic systems traverse the evidence. Ask a security team a simple question: Of the ...
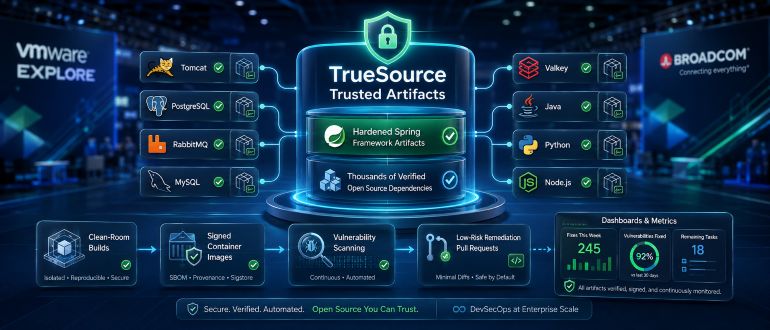
Broadcom Launches TrueSource Service to Secure Spring Framework
Mike Vizard | | AI coding, Apache Tomcat, application security, Bitnami Secure Images, Broadcom, container security, dependency security, devsecops, java, kubernetes, node.js, open source security, open source vulnerabilities, patch management, Python, SBoM, secure software development, software artifacts, Software Supply Chain Security, Spring framework, Spring Security, Tanzu, TrueSource Trusted Artifacts, VMware explore, vulnerability managementBroadcom launches TrueSource Trusted Artifacts to provide hardened Spring dependencies, secure open source packages and automated vulnerability remediation ...

Report Shines Spotlight on 91 Vulnerabilities Fixed in Latest Update to Spring Framework
Mike Vizard | | AI cybersecurity, AI vulnerabilities, application security, Broadcom, CVEs, devsecops, Java security, open source security, open source vulnerabilities, patch management, security automation, software components, Software Supply Chain, sonatype, Spring framework, Spring vulnerabilities, technical debt, virtual patching, vulnerability managementSonatype says 91 Spring vulnerabilities affecting more than 209,000 software components highlight how AI is accelerating vulnerability discovery and creating a new patching challenge for DevSecOps teams ...

Open Source Code Just as Secure as Proprietary Software—If You Manage It Right, Says CISA
 Joab Jackson | | AI security, CISA, federal government, open source software, Software Supply Chain, vulnerability management
Open source can be just as safe as proprietary software, though government agencies (and private enterprises) should take additional measures to secure it properly, according to a new guide published by the ...
Continuous Security in DevSecOps: Moving Beyond One-Time Testing
 James Miller | | automated security, CI/CD pipeline, continuous security, devsecops, penetration testing, SAST/DAST, sdlc, shift left security, software composition analysis (SCA), vulnerability management
Waiting for a single annual pentest to secure your application is like locking your front door only once a year and hoping for the best. In an era where 133 new vulnerabilities are reported every single ...
Rein Security Emerges to Analyze Reachability of Application Vulnerabilities
Mike Vizard | | AI-generated vulnerabilities, API security, application security, continuous vigilance, devsecops, funding, Matan Bar Efrat, performance overhead, security automation, software development, software security testing, vulnerability managementRein Security has emerged from stealth to launch an application security platform capable of determining the reach of a vulnerability based on which libraries and application programming interfaces are actually running in ...